Data and sources
Customer data, repositories, connected systems, and retrieval scope remain subject to enterprise controls and policy-led access rules.
 Book a discovery session
Security & Trust
T-Flux is built for sensitive enterprise operating environments. The security architecture assumes regulated data, controlled users, governed sources, model discipline, and a requirement for audit-ready evidence across the full AI lifecycle.
Data sovereignty
Governed inference
Audit-ready evidence
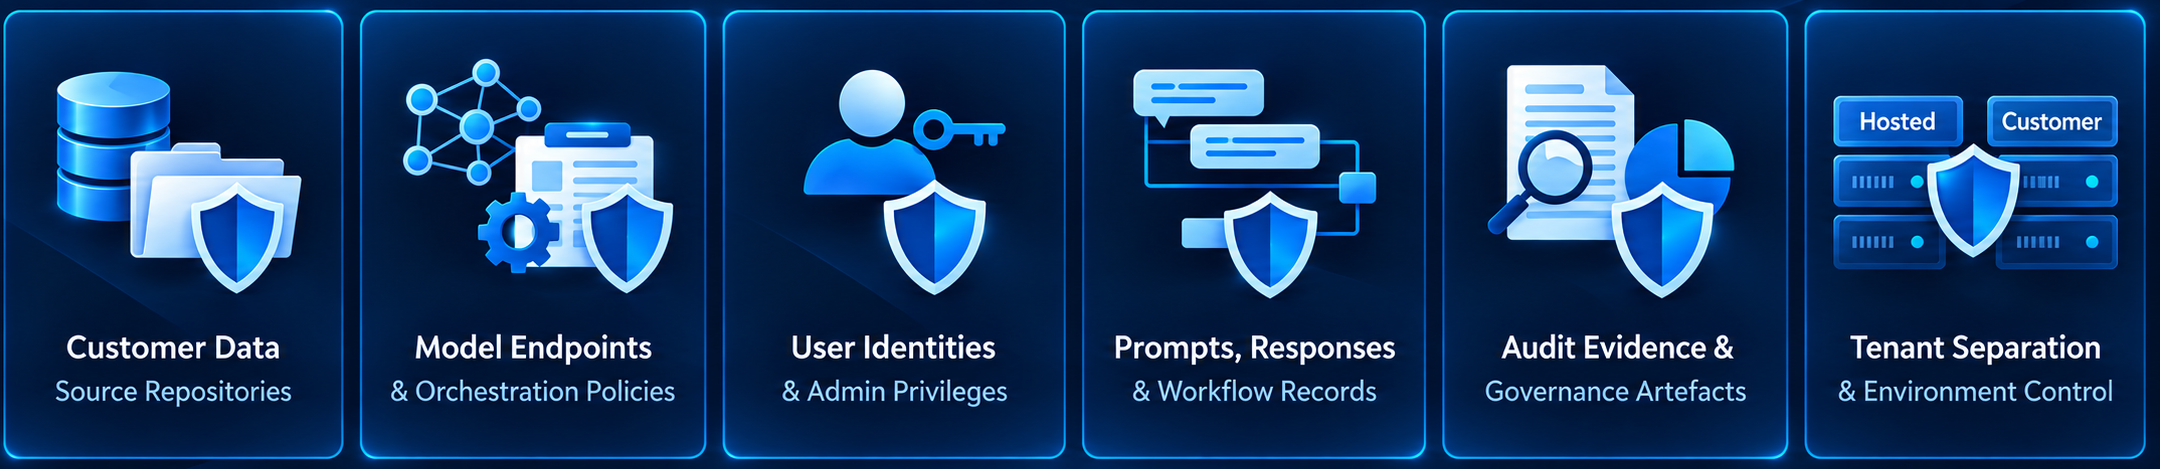
What T-Flux protects
Every part of the AI lifecycle is considered: from the sources and models an organisation trusts to the people, records and controls that make outcomes reviewable.
Customer data, repositories, connected systems, and retrieval scope remain subject to enterprise controls and policy-led access rules.
Approved model endpoints, orchestration policies, and inference paths are governed rather than left to uncontrolled runtime behavior.
Identity, role, privilege, and administrative access are part of the security architecture, not an afterthought.
Prompts, responses, execution records, jobs, and operational events can be captured as controlled evidence.
Evidence packs, governance reports, citations, and policy events support oversight and review.
Hosted or customer-controlled deployment is structured around tenant isolation and enterprise boundary control.
Control model
The security posture is best understood as layered control: deployment, identity, data governance, inference control, and evidence-led oversight.
Supports Solveworx-hosted, private cloud, and on-prem deployment models aligned to data-locality and infrastructure control needs.
MFA, SSO integration, RBAC / ABAC policies, and privileged administrative restriction.
ACL-aware retrieval, source permissions, trust labels, retention logic, masking, and controlled sync boundaries.
Model registration control, orchestrated generation, guardrails, refusal thresholds, and policy-aware response handling.
Traceable logs, operational dashboards, evidence packages, and export-ready governance artefacts.
Private by design
Explore how T-Flux can fit your data perimeter, operating model and oversight requirements.
Book a discovery session